AI/ML detections
Corelight AI/ML detections catch evasive and AI-powered attacks with transparent, evidence-backed conclusions.
Trustworthy AI/ML detections you can tune
Most AI/ML detections ask you to accept a probability score from a black box and move on. Corelight works differently. Across supervised and unsupervised models, every detection traces back to structured, verifiable network evidence. Tune thresholds, build ignore lists, and enable or disable models to suit your environment.
Protect against AI threats
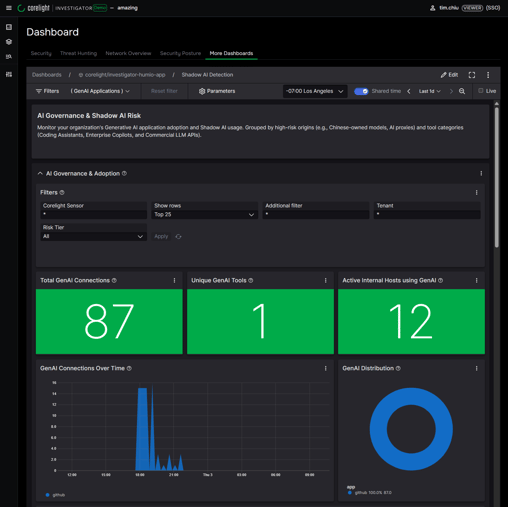
As AI adoption accelerates, so does the risk of Shadow AI and AI-powered attacks. Corelight’s AI Detection and Response (AIDR) solution goes beyond simple visibility. It uses advanced anomaly detection to distinguish routine AI activity from potential threats and policy violations. With AIDR dashboards, gain executive-ready insights into AI tool usage, adoption trends, and compliance risks to proactively manage your exposure.
Fewer false positives, more signal
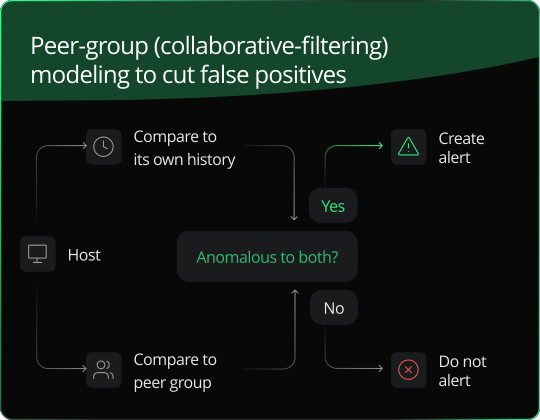
Spend more time on real threats and less time chasing noise. Peer-group modeling measures each host's behavior against its actual role, so an alert fires only when it's truly unusual to both the entity and its peers. Behavioral baselining learns what "normal" looks like on your specific network. To sharpen the signal further, tune detection thresholds and build surgical ignore lists for known business traffic.
Alerts that arrive investigation-ready
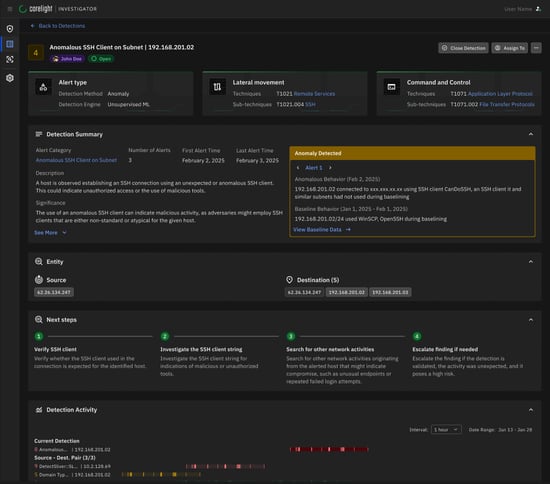
Every detection surfaces with the evidence already attached: Context logs that show behavior before and after the anomaly, correlated across protocols. Move from alert to answer in minutes without pivoting between tools or reconstructing the timeline by hand. Learn more about using Corelight Investigator for incident response.
Explainable, layered detections for confident response
Evidence-backed visibility
Network evidence fuels our AI/ML models, so every anomaly is validated against your network's unique behavior. Because that evidence travels with every alert, you get precise, explainable detections verifiable down to the packet, never an opaque guess.
Layered coverage for defense in depth
No single detection technique catches everything. That is exactly why Corelight NDR layers them. AI/ML detection works in concert with signatures, YARA, threat intelligence, and behavioral analytics. Each layer covers the others’ blind spots, and AI/ML adds the depth to catch what signatures and rules miss.
Contextual incident response
Corelight's AI/ML detections don't just tell you something happened. They surface high-confidence, evidence-rich alerts already correlated with the network telemetry, so you can skip frantic pivoting and move from detection to investigation in a fraction of the usual triage time. That same context feeds directly into response workflows, closing the gap from alert to action and giving your team what it needs to respond decisively.
Operationalize your layered defense strategy
Intrusion Detection
AI/ML uncovers new and evasive threats, while signature detection from Suricata IDS identifies known threats quickly, two essential components of effective multi-layered threat detection.
File Analysis
YARA file analysis adds a powerful detection layer that correlates with AI/ML threat detection to deliver higher-confidence alerts.
Agentic Triage
Agentic Triage correlates alerts across AI/ML and other detection layers, triaging activity from the same entity to deliver trustworthy, evidence-backed results.
Build your platform
AI/ML detection is a subscription-based module that can be purchased with Corelight Sensors. Deploy across air-gapped, hybrid, cloud, or multicloud environments. Enable, manage, and tune AI/ML models through Fleet Manager. Additional AI/ML models are available in our SaaS solution, Investigator. Your team gets detections and evidence working together from day one.
Maximize ROI with services and training from Corelight
Corelight Services and Training puts elite defense within reach by ensuring your team can maximize the value of our Open NDR Platform. From precision deployment and SIEM integration to activity-based training from world-class experts, our services provide the technical guidance needed to accelerate SOC maturity.
-
Accelerate implementation and time to value with health checks
-
Precision engineering for detection calibration and customization
-
Expert-led training and education services
FAQ
What types of threats do the AI/ML detections catch?
They focus on the evasive, insider, and novel threats that slip past signatures and endpoint detection and response (EDR). Coverage includes lateral movement, anomalous remote desktop protocol (RDP) activity, admin-share access, credential attacks, command-and-control (C2) activity, DNS abuse (tunneling and exfiltration), and living off the land (LOTL) techniques. As adversaries weaponize AI to operate at machine speed, models trained on your network's true behavior can catch what static rules were never built to see.
How does Corelight reduce false positives in AI/ML threat detection?
Four mechanisms work together. Peer-group modeling measures each host's behavior against its actual role, so an alert only fires when it's genuinely unusual for both the entity and its peers. Behavioral baselining learns what normal looks like on your specific network, not a generic template. Granular tuning lets you sharpen the signal further. High-fidelity, validated threat intelligence adds another layer of precision beyond noisy open-source feeds. The result is that analysts spend more time on real threats and less time chasing noise.
How do AI/ML threat detections fit into a multi-layered NDR strategy?
AI/ML detections are one layer in Corelight’s Open NDR Platform. They work in concert with signatures, YARA file analysis, indicators of compromise (IOCs) from threat intelligence, and behavioral analytics. Each layer covers the others' blind spots, giving you true defense in depth and broader MITRE ATT&CK coverage. AI/ML adds the depth needed to surface the evasive and novel threats that signatures and rules miss.
Do the AI/ML detections run on-sensor or in the cloud?
Many detections run directly on-sensor, with no cloud dependency. These lightweight, efficient models run on Corelight Sensors, lowering infrastructure costs and removing the need for centralized cloud analytics servers. Detection logic stays open, inspectable, and customizable, and telemetry is collected passively, out-of-band, so there's no risk of network downtime. Some AI/ML models require the visibility and data from multiple sensors, and those detections run in our SaaS solution, Investigator.
Will AI replace my analysts?
No. Corelight's AI is built to complement human judgment, not replace it. By automating data gathering, correlation, and initial analysis, it removes the manual grind that drives burnout and turnover, freeing your team to focus on proactive threat hunting and decisive response. You get AI-driven efficiency and stronger analyst retention, not a black box asking for blind faith.