


Detect evasive threats with ML
ML-powered behavioral and anomaly detections find evasive threats with context-aware precision, relying on an open and evidence-first model to reduce false positives and manual tuning.

Here’s how
Corelight leverages diverse machine learning techniques for its multi-layered threat detection, incorporating both traditional models and advanced deep learning models like CNNs, RNNs, and recommender systems like NCF.

Cut your triage time in half
Maximize SOC efficiency with automated daily triage that investigates the last seven days of activity for your environment's top entities. By running specialized queries and applying transparent expert-authored playbooks, agentic workflows empower you to take decisive action with defensible logic.

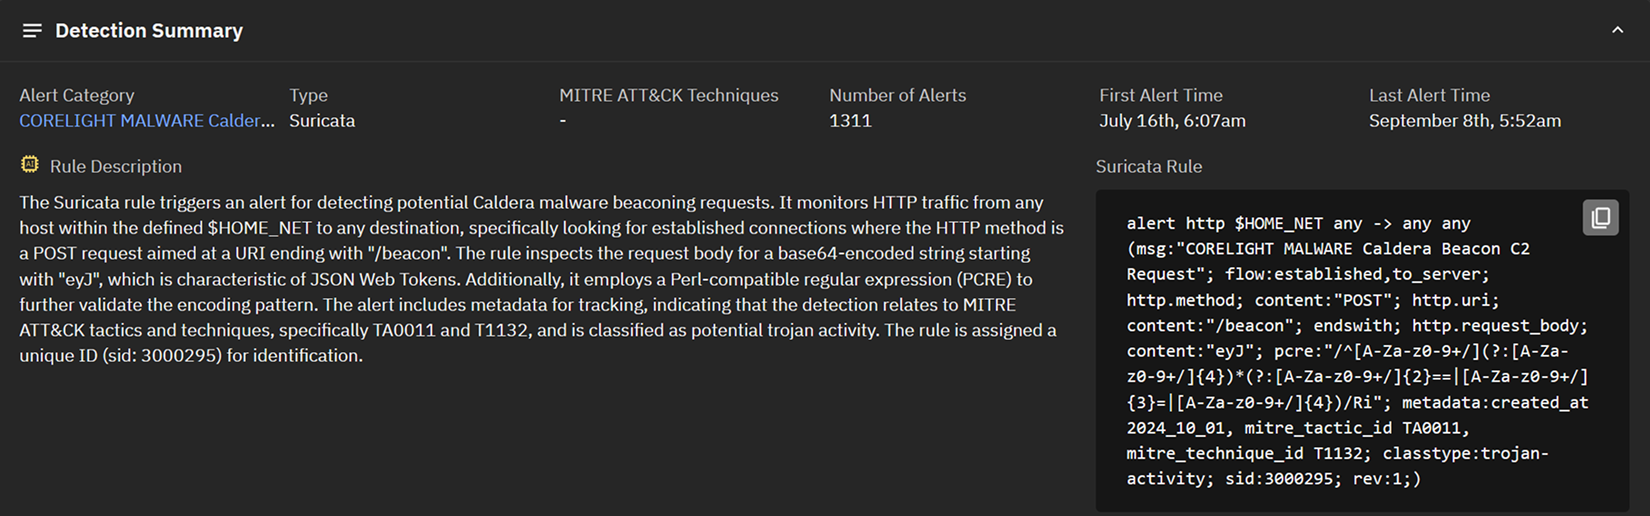
AI assistance
Uplevel SOC analyst skills with generated log summaries, response guidance, policy helpers, chat, and NLQ (Natural Language Query). Ask questions about your network in plain English and get evidence-backed answers instantly, no query syntax needed.
Agentic triage
Improve mean times and enable automation for threat detection and response with agentic triage that streamlines workflows for correlation, investigation, verdicts, and findings summaries.
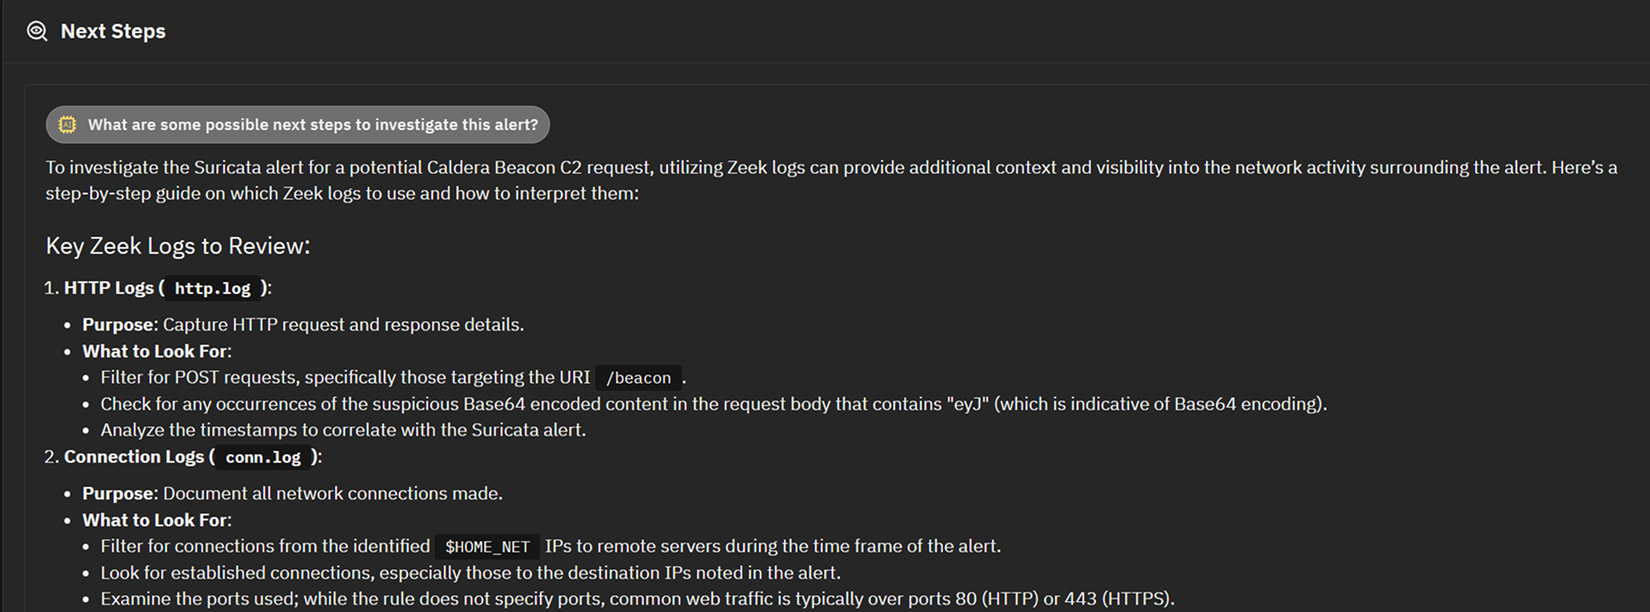
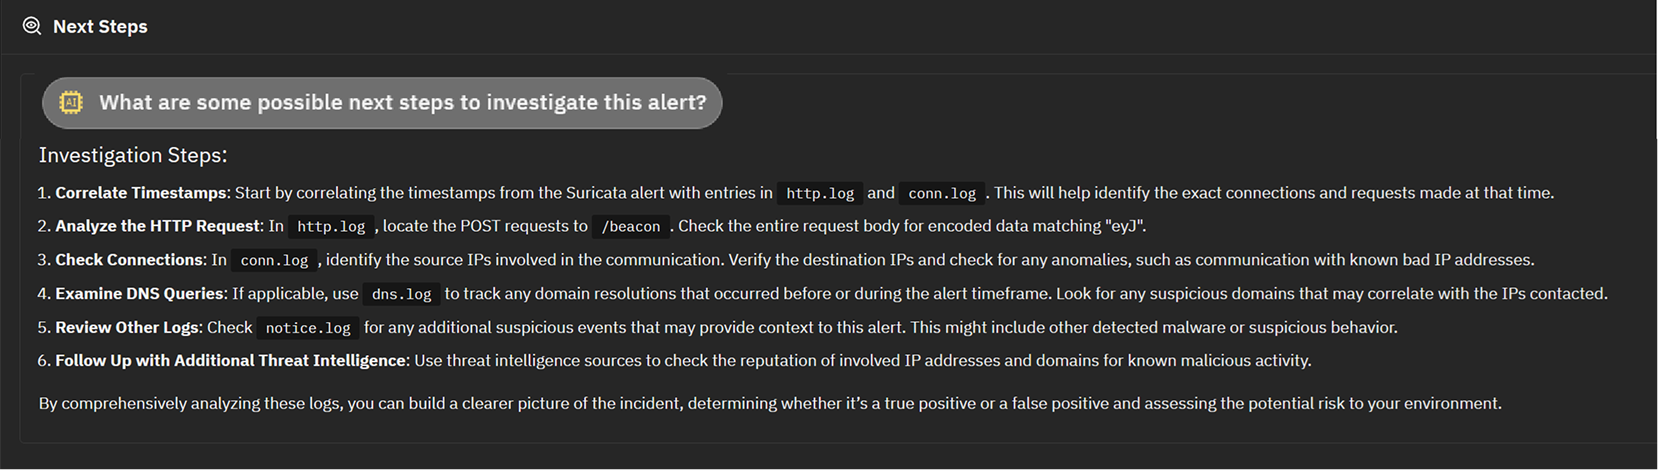
AI investigation
Guide investigations by condensing a complex process into a set of actionable next steps and automating alert scoring and prioritization with powerful searches for IOCs, entities, third-party alerts, and A2A questions.

Accelerate your transition to an AI SOC
Corelight provides the only NDR solution that powers the SOC ecosystem with open, standards-based evidence and a Model Context Protocol (MCP) server purpose-built for AI orchestration and seamless integration with existing SOC workflows.
Capture a decade of Corelight's network forensics expertise into structured, exportable artifacts, including triage playbooks, investigation decision trees, and entity pivoting guides with our Agent Builder Library. Teams building their own AI agents, enriching SOAR workflows, or operating in air-gapped environments can ingest this knowledge directly.


Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
The team is readily available for any question or concern. They are network security professionals who know what they are doing.
Cybersecurity Engineer – Education
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
I like that there was minimal management of the policies that was needed to get great coverage.
Information Technology Specialist – Manufacturing
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
Exceptional product and product support. Functionality and UI/UX is easy to grasp. Utility of the product is usable instantly.
Cybersecurity Specialist – Government
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
It performs well at line speeds and the resulting metadata is highly valuable in triaging suspicious activities.
R&D Lead for Cybersentry – Government
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
The feature set is amazing, the set up was easy (easy-ish!) and it just WORKS.
Director, IT Security and Risk Management – Government